The CrowdStrike outage: how one bad update crashed 8.5 million computers
On 19 July 2024 a faulty security update from CrowdStrike crashed Windows machines at airlines, hospitals and banks worldwide. The cause was a mismatch of 21 fields against 20. Two years on, Delta's lawsuit is still in discovery, and Microsoft is moving security software out of the Windows kernel.
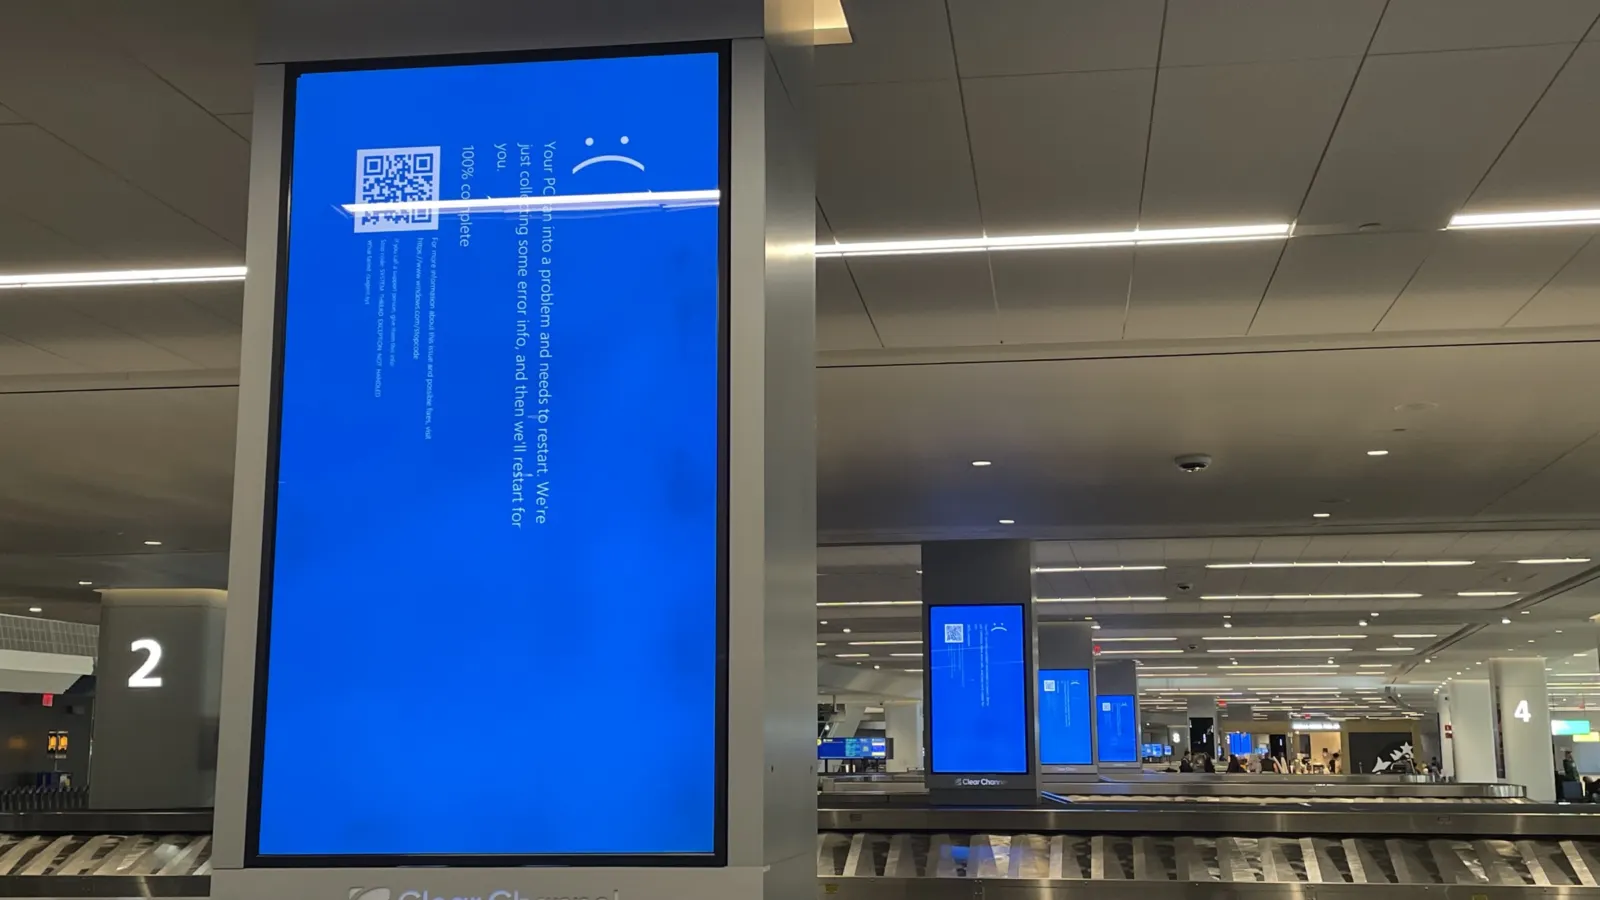
AUSTIN, Texas At 04:09 UTC on Friday 19 July 2024, the cybersecurity company CrowdStrike released a configuration update for its Falcon security software on Windows computers. Machines that received it crashed to the “blue screen of death”. CrowdStrike fixed the update at 05:27 UTC 1. “This issue is not the result of or related to a cyberattack,” the company said 1.
Microsoft estimated that 8.5 million Windows devices were affected, “less than one percent of all Windows machines” 2. Because so many of them ran airline check-in systems, hospital records and bank branches, the effect was global. Airlines lost access to booking and check-in systems and thousands of flights were cancelled; hospitals including Mass General Brigham cancelled non-urgent surgeries and visits; banks and broadcasters were disrupted 3.
Twenty-one against twenty
CrowdStrike’s own root cause analysis, published on 6 August 2024, traced the crash to a mismatch. A new type of detection template, introduced in February 2024, defined 21 input fields, but the code that fed it supplied only 20. The mismatch went unnoticed until the 19 July update used the 21st field for the first time. “The Content Interpreter expected only 20 values,” the company wrote; reading the missing 21st caused an out-of-bounds memory read that crashed the system 4. The analysis said the number of fields had not been checked when the software was built, a runtime bounds check was missing, and a validation tool contained a logic error 4. By 29 July about 99% of affected Windows sensors were back online 45.
Testifying to a House homeland security subcommittee in September 2024, CrowdStrike’s senior vice-president Adam Meyers acknowledged that “the updates were distributed to all customers in one session” and said the company was “now treating the content updates as code”, with staged roll-outs and customer control over timing 67.
How it unfolded
-
Key moment. Faulty update released; Windows machines crash worldwide.
-
CrowdStrike pulls the update.
-
About 99% of affected sensors back online.
-
Root cause analysis published.
-
CrowdStrike testifies to Congress.
-
Key moment. Delta sues CrowdStrike; CrowdStrike countersues.
-
Georgia judge lets parts of Delta’s case proceed.
-
Shareholder suit dismissed, with leave to amend.
-
Key moment. Microsoft’s endpoint security platform reaches general availability.
The bill
The insurer Parametrix estimated direct losses for US Fortune 500 companies, excluding Microsoft, at $5.4 billion, only 10% to 20% of it covered by cyber insurance 8. Delta Air Lines recovered more slowly than other carriers 9: it cancelled about 7,000 flights over five days and said the outage cut its revenue by $380 million and added $170 million in costs 910.
In October 2024 Delta sued CrowdStrike in Georgia, seeking more than $500 million. “If CrowdStrike had tested the Faulty Update on even one computer before deployment, the computer would have crashed,” its complaint said 9. CrowdStrike countersued, saying Delta’s losses were “the result primarily of Delta’s own negligence” 9. In May 2025 a Fulton County judge allowed Delta’s claims including negligence and computer trespass to proceed, while dismissing others 1011. CrowdStrike’s lawyer said he was confident damages would be limited to the “single-digit millions of dollars” 10. The company’s latest quarterly filing says discovery is continuing 12. No court has found CrowdStrike liable.
Other suits have fared less well. Passenger class actions were dismissed in 2025, a decision upheld on appeal in May 2026; the passengers have asked the US Supreme Court to hear the case 1213. A shareholder suit was dismissed in January 2026, with permission to file an amended complaint; the judge found the plaintiffs had “failed to plausibly plead a strong inference of scienter”, or intent 14. In June 2026 the US Department of Transportation closed its investigation into Delta’s handling of the disruption without seeking penalties 15.
The kernel
The outage reopened a long-running question: should security software run inside the core of the operating system, the kernel, where a single fault can bring down the whole machine? In November 2024 Microsoft said it would let security products “run in user mode just as apps do” 16. On 17 November 2026 it announced that its Windows endpoint security platform was “reaching general availability on Windows 11”, a step towards reducing security vendors’ reliance on kernel drivers 17.
Why it matters
The CrowdStrike outage was not a hack. It showed that the software meant to protect computers had become a single point of failure for airlines, hospitals and banks across the world, and that one untested change could take them down at once. The lasting response is engineering rather than litigation: staged updates, and a slow move of security software out of the part of Windows where a mistake is fatal.
Sources and references
- Official documentCrowdStrike, “Technical Details: Falcon Content Update for Windows Hosts”, 20 July 2024. Link
- Official documentMicrosoft, “Helping our customers through the CrowdStrike outage”, 20 July 2024. Link
- ArticleAssociated Press (via WBTV), “A faulty software update causes havoc worldwide for airlines, hospitals and governments”, 19 July 2024. Link
- Official documentCrowdStrike, “External Technical Root Cause Analysis — Channel File 291”, 6 August 2024. Link
- Official documentCrowdStrike, “Channel File 291 Root Cause Analysis available”, 6 August 2024. Link
- ArticleThe Record (Recorded Future News), “CrowdStrike tells Congress of two process changes to address July outage incident”, 25 September 2024. Link
- Official documentHouse Committee on Homeland Security, “ICYMI: Committee Examines CrowdStrike Processes in First Congressional Hearing”, 26 September 2024. Link
- ReportParametrix, “CrowdStrike to cost Fortune 500 $5.4 billion”, 24 July 2024. Link
- ArticleCNBC, “Delta sues CrowdStrike over July outage”, 25 October 2024. Link
- ArticleReuters (via KSL), “Delta can sue CrowdStrike over computer outage that caused 7,000 canceled flights”, 19 May 2025. Link
- ArticleThe Register, “Judge allows Delta’s lawsuit against CrowdStrike to proceed with millions in damages on the line”, 21 May 2025. Link
- Official documentCrowdStrike / SEC, “CrowdStrike Holdings Form 10-Q (quarter ended 31 July 2026) — Commitments and Contingencies”. Link
- Court documentSupreme Court of the United States, “Docket No. 26-355, del Rio v. CrowdStrike, Inc.”, 16 September 2026. Link
- ArticleThe Register, “CrowdStrike shareholders lose battle to recoup losses from 2024 outage”, 14 January 2026. Link
- ArticleReuters (via The Star), “US closes probe into 2024 Delta Air Lines meltdown sparked by CrowdStrike outage”, 16 June 2026. Link
- Official documentMicrosoft, “Windows security and resiliency: Protecting your business”, 19 November 2024. Link
- Official documentMicrosoft, “Windows security at Ignite 2026”, 17 November 2026. Link
Sources and references are provided for transparency and further reading. Allegations and claims are attributed to their respective sources. Triple Frontiers distinguishes reported allegations from independently established facts.
The Frontier Brief
The week’s essential international reporting and new investigations, every Friday.