ToolShell: how China-linked hackers exploited SharePoint servers worldwide
In July 2025 attackers exploited flaws in self-hosted Microsoft SharePoint servers, compromising more than 400 systems according to Eye Security. Microsoft blamed China-based groups, one of which deployed ransomware; Beijing denied involvement. More than a year on, the ransomware group is still targeting SharePoint.
WASHINGTON In mid-July 2025 attackers began breaking into on-premises Microsoft SharePoint servers around the world through a chain of flaws that became known as “ToolShell” 12. Eye Security, which says it was the first to spot the mass exploitation on the evening of 18 July, found more than 400 systems actively compromised 23. Microsoft blamed two Chinese state-backed groups and a third China-based actor that went on to deploy ransomware 1. China rejected the accusations 45.
The attacks hit self-hosted SharePoint Server, in its Subscription Edition, 2019 and 2016 versions; SharePoint Online in Microsoft 365 was not affected 16.
A patch that did not hold
The chain combined a spoofing flaw, CVE-2025-49706, with a remote code execution flaw, CVE-2025-49704 1. According to Eye Security, both had been presented at the Pwn2Own Berlin hacking contest in May 2025 and were patched by Microsoft on 8 July 2. Two related flaws, CVE-2025-53771 and CVE-2025-53770, were bypasses of those fixes 17.
Microsoft’s analysis suggested exploitation attempts began as early as 7 July 1. Palo Alto Networks’ Unit 42 recorded exploitation attempts from 17 July 8. Eye Security said it “stumbled upon a weaponized Pwn2Own exploit being used in the wild”, and recorded a test wave on 17 July, a “widely successful” wave on 18 July and further waves on 19 July and from 21 July 2.
On 19 July Microsoft said: “Microsoft is aware of active attacks targeting on-premises SharePoint Server customers” 6. It said its July security update had partially addressed the vulnerabilities 6. By 22 July updates were available for all supported versions, and Microsoft told customers: “Customers should apply these updates immediately.” 1
Patching was not enough on its own. Microsoft and the US Cybersecurity and Infrastructure Security Agency (CISA) told administrators to rotate the servers’ ASP.NET machine keys and restart IIS, because attackers had been stealing the keys 19. Unit 42 went further: “If you have SharePoint on-premises exposed to the internet, you should assume that you have been compromised.” 8
Washington’s response
CISA said on 20 July that it was “aware of active exploitation of a spoofing and RCE vulnerability chain” 9. It added CVE-2025-53770 to its Known Exploited Vulnerabilities catalogue that day and gave federal agencies until 21 July to act 7. On 22 July it added CVE-2025-49704 and CVE-2025-49706, with a deadline of 23 July 7. The required actions included disconnecting public-facing SharePoint versions that had reached end of life, including SharePoint Server 2013 and earlier 79.
CISA set the federal deadlines through its catalogue of known exploited vulnerabilities 79. On 6 August it published an analysis of files recovered from incidents, including two .NET files it described as machine key retrieval tools and several web shells 10.
Who was hit
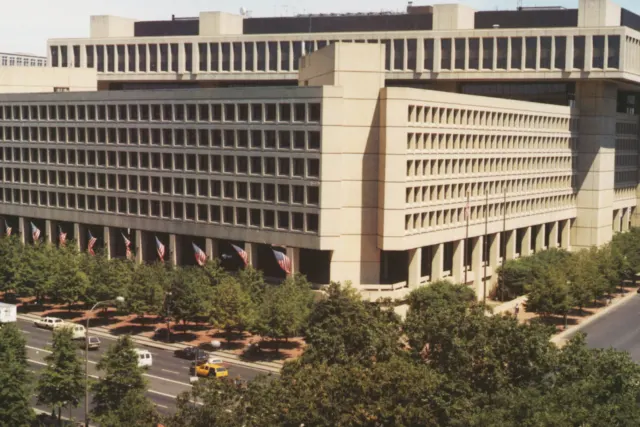
The US Department of Energy confirmed that the exploitation “began affecting the Department of Energy, including the NNSA”, its nuclear weapons agency, on Friday 18 July 1112. Ben Dietderich, the department’s press secretary, said: “The Department was minimally impacted” 11. He said that a very small number of systems were affected and attributed this to the department’s widespread use of Microsoft 365 cloud services 11. “All impacted systems are being restored,” the department said 12. Sources told Bloomberg there was no evidence that sensitive or classified information had been compromised 1112.
A National Institutes of Health representative confirmed to Reuters that one of its servers had been compromised 5. “Additional servers were isolated as a precaution,” the representative said 5. Nextgov, citing sources, reported that the Department of Homeland Security was also hit 5. The Record later reported that DHS had confirmed being affected 13. The Department of Education, Florida’s Department of Revenue and the Rhode Island General Assembly were named in reports based on anonymous sources 113.
Eye Security scanned more than 23,000 SharePoint servers to reach its count of more than 400 compromised systems, up from about 100 organisations over the weekend of 19 and 20 July 25. “There are many more, because not all attack vectors have left artefacts that we could scan for,” Vaisha Bernard of Eye Security told Reuters 5. In October 2025 researchers at Symantec and Carbon Black reported intrusions at a Middle East telecoms company, two government departments in an African country, two government agencies in South America and a US university 13.
How it unfolded
-
Earliest exploitation attempts, according to Microsoft’s analysis {p1}
-
Microsoft’s July update partially fixes the flaws {p2}{p6}
-
Key moment. Mass exploitation wave; Storm-2603 begins deploying ransomware; Energy Department affected {p6}{p1}{p8}
-
Key moment. Microsoft confirms active attacks and publishes guidance {p2}
-
Key moment. CISA alert; CVE-2025-53770 added to exploited-flaws catalogue with a one-day deadline {p3}{p4}
-
Key moment. Microsoft names Linen Typhoon, Violet Typhoon and Storm-2603 {p1}
-
Key moment. Energy Department confirms NNSA affected; China rejects ‘smears’ {p8}{p12}
-
Eye Security count passes 400 compromised systems; NIH confirms a server breach {p10}{p11}
-
CISA publishes malware analysis of recovered files {p5}
-
Microsoft confirms curbs on Chinese MAPP partners {p13}
-
Symantec research reports victims in the Middle East, Africa and South America {p14}
-
Key moment. Symantec says the Warlock group is still exploiting SharePoint {p15}
Espionage groups and ransomware
On 22 July Microsoft named Linen Typhoon and Violet Typhoon, which it describes as Chinese nation-state actors, and Storm-2603, which it assessed with moderate confidence to be China-based 1. It describes Linen Typhoon as active since 2012 and focused on stealing intellectual property, and Violet Typhoon as active since 2015 and focused on espionage 1.
Microsoft said that, starting on 18 July, it had observed Storm-2603 deploying Warlock ransomware through the SharePoint flaws 15. After getting in, the group stole credentials and changed Group Policy settings to spread the ransomware 1. Microsoft said it had seen the group use Warlock and LockBit before, but added: “Microsoft is currently unable to confidently assess the threat actor’s objectives.” 1
Unit 42 separately reported a ransomware strain it called 4L4MD4R in a failed attack on 27 July 2025. It assessed with moderate confidence that the cluster it tracks overlaps with Storm-2603 8.
China’s denial and Microsoft’s leak inquiry
Asked by Reuters on 23 July about the attacks, Chinese foreign ministry spokesperson Guo Jiakun said he was not aware of the specific situation 4. “Cybersecurity is a common challenge faced by all countries and should be addressed jointly through dialogue and cooperation,” he said (translated from Chinese) 4. He added that China “consistently opposes and cracks down on hacking activities in accordance with the law” and “opposes smearing and slandering China on the pretext of cybersecurity issues” (translated from Chinese) 4.
In August 2025 Microsoft said it had, since July, stopped giving proof-of-concept code to partners in its Microsoft Active Protections Program (MAPP) in countries that require companies to report vulnerabilities to their governments, including China 14. Bloomberg had reported that Microsoft was investigating whether details of the flaws leaked from MAPP partners 14. Microsoft did not disclose the findings; its spokesperson David Cuddy said there were “multiple working theories on the cause” 14. The Chinese embassy in Washington said it was not familiar with the details 14.
Where things stand
Microsoft has not published the outcome of its MAPP inquiry 14.
The ransomware activity has continued. On 1 October 2026 Symantec reported that the group it calls Longlegs, which it says is also known as Storm-2603 and develops Warlock, had attacked at least four organisations in Portuguese- and Spanish-speaking countries in Europe, Africa and Latin America over the previous two months 15. They included a water utility and a telecoms provider 15. In one case a web shell was planted on a SharePoint server on 22 July 2026, and Warlock was deployed on at least 33 machines on 31 July 15. “The group continues to favor SharePoint-related vulnerabilities to gain initial access to targeted organizations,” Symantec said 15.
SharePoint has stayed a target. Between March and September 2026 CISA added eight more SharePoint vulnerabilities to its catalogue of flaws exploited in attacks, one of them flagged as used in ransomware campaigns 7.
Why it matters
ToolShell showed how fast a disclosed flaw in self-hosted software can become a mass compromise. Exploitation began before a complete fix was available, and stolen machine keys meant that patching alone did not remove intruders 169. The campaign mixed state espionage with ransomware and reached US government bodies, including the nuclear weapons agency, the NNSA 111. It also led Microsoft to limit what it shares with security partners in China 14. More than a year later, the group linked to the ransomware is still using SharePoint flaws to get in 15.
Sources and references
- Official documentMicrosoft Threat Intelligence, “Disrupting active exploitation of on-premises SharePoint vulnerabilities”, 22 July 2025. Link
- ReportEye Security, “SharePoint under siege”, 19 July 2025. Link
- ArticleSecurityWeek, “ToolShell Attacks Hit 400 SharePoint Servers, US Government Victims Named”, 24 July 2025. Link
- Official documentMinistry of Foreign Affairs of the People’s Republic of China, “2025年7月23日外交部发言人郭嘉昆主持例行记者会”, 23 July 2025. Link
- ArticleDawn / Reuters, “Microsoft says some SharePoint server hackers now using ransomware (Reuters)”, 24 July 2025. Link
- Official documentMicrosoft Security Response Center, “Customer guidance for SharePoint vulnerability CVE-2025-53770”, 19 July 2025. Link
- Official documentCISA, “Known Exploited Vulnerabilities Catalog (JSON feed, version 2026.11.17)”, 17 November 2026. Link
- ReportPalo Alto Networks Unit 42, “Active Exploitation of Microsoft SharePoint Vulnerabilities: Threat Brief”, 31 July 2025. Link
- Official documentCISA, “UPDATE: Microsoft Releases Guidance on Exploitation of SharePoint Vulnerabilities”, 20 July 2025. Link
- Official documentCISA, “MAR-251132.c1.v1 Exploitation of SharePoint Vulnerabilities (AR25-218A)”, 6 August 2025. Link
- ArticleBleepingComputer, “US nuclear weapons agency hacked in SharePoint attacks”, 23 July 2025. Link
- ArticleFox News, “Chinese-linked hackers breached US nuclear agency, officials say”, 23 July 2025. Link
- ArticleThe Record (Recorded Future News), “SharePoint ToolShell bug used to breach governments in Africa, South America”, 22 October 2025. Link
- ArticleClaims Journal / Bloomberg, “Microsoft Curbs Early Access for Chinese Firms to Notifications About Cybersecurity Flaws (Bloomberg)”, 20 August 2025. Link
- ReportSymantec Threat Hunter Team (Broadcom), “Warlock Ransomware Attackers Hit Water and Telecom Operators”, 1 October 2026. Link
Sources and references are provided for transparency and further reading. Allegations and claims are attributed to their respective sources. Triple Frontiers distinguishes reported allegations from independently established facts.
The Frontier Brief
The week’s essential international reporting and new investigations, every Friday.